Native x86/x64 code protection
Protect Critical Windows Code with Virtualization and Mutation
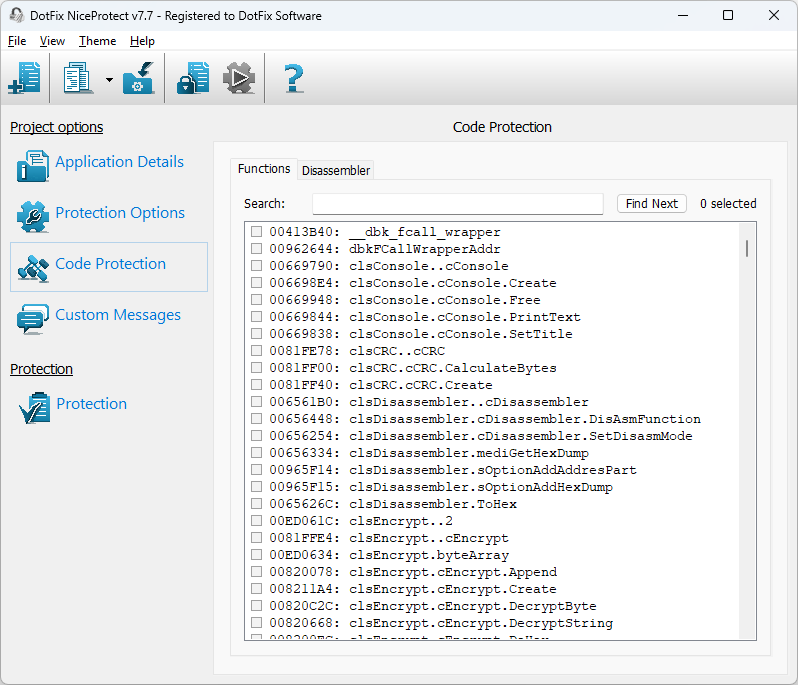
DotFix NiceProtect transforms selected native instructions instead of applying the same protection indiscriminately to an entire program. Choose functions through compiler-generated MAP data or mark an exact source-code region with the SDK.
Two ways to select the code that matters
SDK markers for exact x86 regions
Place start and end markers around a critical block in Delphi, Free Pascal, C/C++ or Visual Basic source code. NiceProtect locates the compiled markers automatically and protects the enclosed 32-bit code. SDK markers are currently available for x86 applications only.
MAP files for x86 and x64 functions
Enable MAP-file generation in your compiler settings and rebuild the application. Compilers normally write the MAP file alongside the corresponding EXE, DLL or OCX. NiceProtect uses its function names and addresses to let you select native functions without changing their source. MAP-based selection supports both x86 and x64 binaries.
Why protecting the function code matters
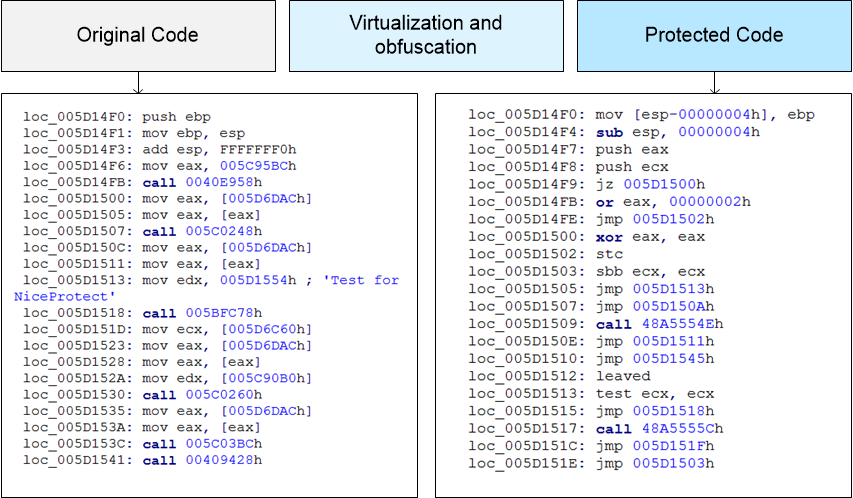
With MAP-based selection, NiceProtect transforms code starting at the function entry. The original protected block is filled with junk code, and execution jumps into a protection section containing virtualized and mutated instructions. If protection stops before the end of the function, execution jumps back to the remaining native code.
This breaks the recognizable entry point on which automated function discovery, decompilation and dependency-graph analysis depend. A reverse engineer cannot simply follow the original instruction stream through the replaced region; understanding the protected logic requires manual analysis and devirtualization.
The transformed region may be the entire function or the part supported by the current protection engine. The protection log reports the actual number of bytes transformed. For an exact critical region deeper inside an x86 function, use SDK markers.
Virtualization and mutation protect code differently
Virtualization translates supported instructions into a custom virtual-machine instruction set executed by the protected application. Mutation replaces native instructions with more complex equivalent sequences and mixes them with generated code. NiceProtect can combine both approaches, making the boundary between transformed native code and virtual-machine transitions harder to identify.
The built-in x86/x64 disassembler lets you inspect the original function and review generated protected variants before producing a release build.
Architecture and deployment scope
MAP-based native-code protection supports Windows x86 and x64 applications. SDK markers currently support x86 code. NiceProtect does not protect native ARM binaries; beginning with version 26.1, protected x86 and x64 applications can run on Windows on Arm through Microsoft’s built-in Prism emulation.
Use the trial with a real build: instruction patterns, exception handling and control flow determine how much code can be transformed. The protection log records the result, and the protected application should always be tested through its normal workflows before release.
Implementation guides and examples
See the version 26.1 engine overview, the illustrated virtualization article, the official MAP-file guide and the SDK marker reference.
Protect the code an attacker would target first
Test MAP-based function selection or x86 SDK markers with your own compiled application.